A professional at a laptop reviewing digital trust metrics displayed on an interactive holographic interface.
Photo · geminiDigital trust is no longer a buzzword; it is the backbone of every modern online interaction, from a routine retail checkout to a complex multi-cloud enterprise workflow. As businesses embed security controls deeper into distributed networks, human identities, and edge devices, a new class of digital trust tools has emerged to guarantee that enterprise data, transactions, and system identities stay genuine. Platforms like ShouldEye, along with its automated intelligence layer - EyeQ, help organizations cut through vendor claims and verify software before entering long-term contracts. This guide walks you through the core concepts, the practical checklist you need before signing a vendor contract, and where the hidden operational risks often hide.
Why Digital Trust and Machine Identity Management Matter Today
At its core, digital trust is the foundational framework, software ecosystem, and governance practices that enable confidence between modern web systems and their stakeholders. Authoritative guidance from the National Institute of Standards and Technology (NIST) highlights that system resilience requires continuous, auditable verification across all network touchpoints. When an end user clicks "pay now," they expect their payment details to be strongly encrypted, their credentials to be protected against interception, and the merchant to honor the transaction. A breach of any of these expectations erodes market reputation and triggers costly legal fallout.
Two industry developments are accelerating the immediate need for stronger digital trust tools:
Cryptographic identity verification: Every single digital action must be tied to a verified legal identity through robust cryptographic proof.
Machine identity management: Modern connected devices, microservices, cloud containers, and APIs require automated credentialing and monitoring, not just human users.
If you are evaluating modern digital trust tools, start by asking, "Does this tool protect both human and machine endpoints, and does it do so in a transparent manner?" Using ShouldEye and EyeQ allows risk teams to benchmark vendor claims against these baseline standards.
Core Components of Next-Gen Cryptographic Identity Verification
Digital trust relies on specific core technical components. Rather than relying on simple passwords, contemporary architectures combine rigorous verification protocols across several complementary functional layers:
Cryptographic identity verification links digital actions directly to a legally verified party, preventing spoofing and impersonation attacks. Alongside this, machine identity management governs security certificates and operational keys across containers, virtual machines, and backend APIs to stop lateral movement during security breaches. Physical security is reinforced by hardware-backed passkeys, which leverage tamper-resistant tokens to eliminate credential harvesting. Finally, an objective digital trust assessment provides teams with structured methodologies to benchmark their current maturity and isolate architectural gaps before auditors arrive.
These foundational pillars are clearly reflected in prominent cybersecurity vendors:
CyberArk delivers specialized solutions for machine identity management that integrate directly into network-level access controls.
Yubico provides standardized hardware-backed passkeys designed to resist advanced phishing schemes and fulfill rigorous access programs.
ISACA offers a structured digital trust assessment framework to help security teams identify procedural gaps and measure compliance.
✨ Quick Trust Check
How to Evaluate Digital Trust Tools for Enterprise Security
When you sit through a technical vendor demonstration, a rigorous checklist keeps your discussion focused on risk-relevant facts. Conducting a thorough digital trust assessment before procurement prevents costly migration mistakes.
1. Verify Cryptographic Identity Verification Standards
Determine whether the vendor relies on audited algorithms, including RSA-4096 and ECC-P-256. Verify whether cryptographic keys reside inside dedicated hardware security modules or trusted execution environments. Robust digital trust tools must never store unencrypted key material in standard file storage.
2. Check Machine Identity Management Coverage
Map every single asset type that requires active certificates, including Kubernetes clusters, serverless functions, IoT gateways, and database pipelines. CyberArk machine identity management workflows demonstrate that continuous device verification across zero trust architecture requires complete visibility into active credentials.
3. Assess Hardware-Backed Passkeys and Authentication Controls
Confirm whether the solution natively supports FIDO2 and WebAuthn standards. Requiring hardware-backed passkeys ensures that even if credentials leak, unauthorized entry remains blocked at the gateway.
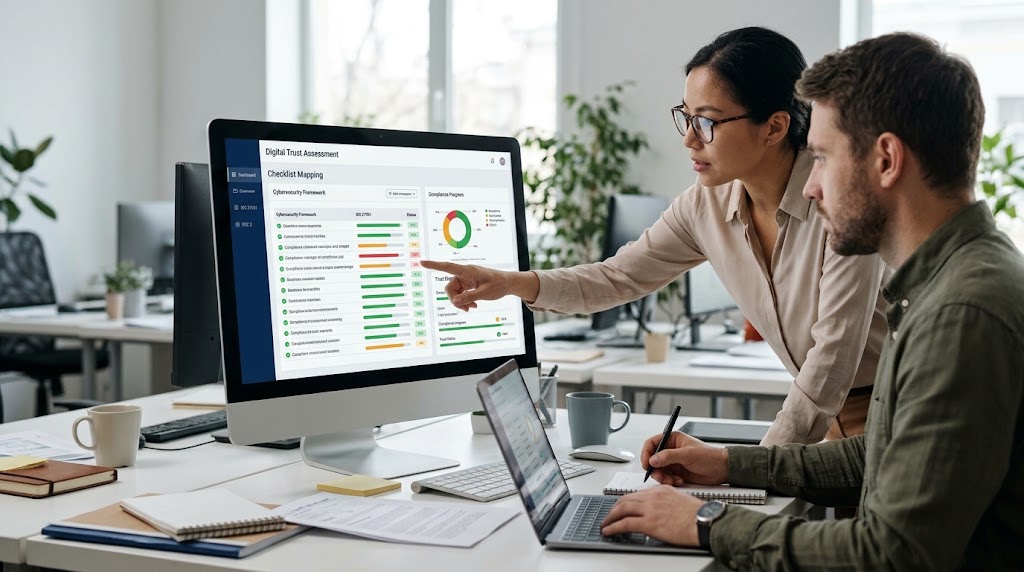
4. Review Digital Trust Assessment and Compliance Reporting
Ensure the vendor dashboard maps directly to recognized cybersecurity frameworks such as ISO 27001 or SOC 2. ISACA guidance underscores that a repeatable digital trust assessment process is essential for compliance audits and third-party risk management.
5. Examine Policy Transparency and Data Handling
Request the full data processing addendum. You must confirm log retention windows, geographical data boundaries, and internal access privileges for vendor engineers.
6. Evaluate API Openness and Zero Trust Architecture
Modern enterprises operate complex security stacks. Your digital trust tools must expose well-documented REST or GraphQL APIs to feed event telemetry directly into SIEM systems, identity governance hubs, and CI/CD pipelines.
7. Scrutinize Support SLAs and Product Roadmaps
Demand a published update schedule and clearly defined service level agreements for critical vulnerability remediation. Transparent digital trust tools publish their product lifecycle timelines openly.
⚡ Reality Check
- Pricing transparency: Most digital‑trust vendors keep pricing behind sales calls, making cost forecasting difficult.
- Performance benchmarks: Independent latency or scalability data is rarely published, so you must request proof‑of‑concept results.
- Roadmap visibility: Future feature releases are often undisclosed, leaving long‑term compatibility uncertain.
- Adoption metrics: Exact market‑share or customer‑base numbers are not publicly available for many providers.
Common Red Flags in Digital Trust Tools Procurement
Even polished sales collateral can obscure severe functional drawbacks. During vendor evaluation, keep an eye out for these frequent issues:
Vague pricing structures: Missing pricing schedules often indicate punitive usage-based tiers that inflate dramatically as your API consumption increases.
Missing performance benchmarks: When vendors omit latency benchmarks, their encryption proxies or identity lookups may degrade user response times.
Unspecified update cycles: The absence of a transparent engineering roadmap leaves buyers vulnerable to unpatched dependencies.
Limited public customer evidence: A lack of verifiable production deployments means your team becomes an untested beta site for unproven machine identity management systems.
Unsubstantiated compliance claims: Broad assertions of total regulatory adherence without third-party attestation reports represent significant operational liability.
If an enterprise vendor cannot resolve these concerns with concrete technical documentation, treat the software as an operational liability rather than an enterprise-ready solution.
How ShouldEye Streamlines Vendor Risk Intelligence
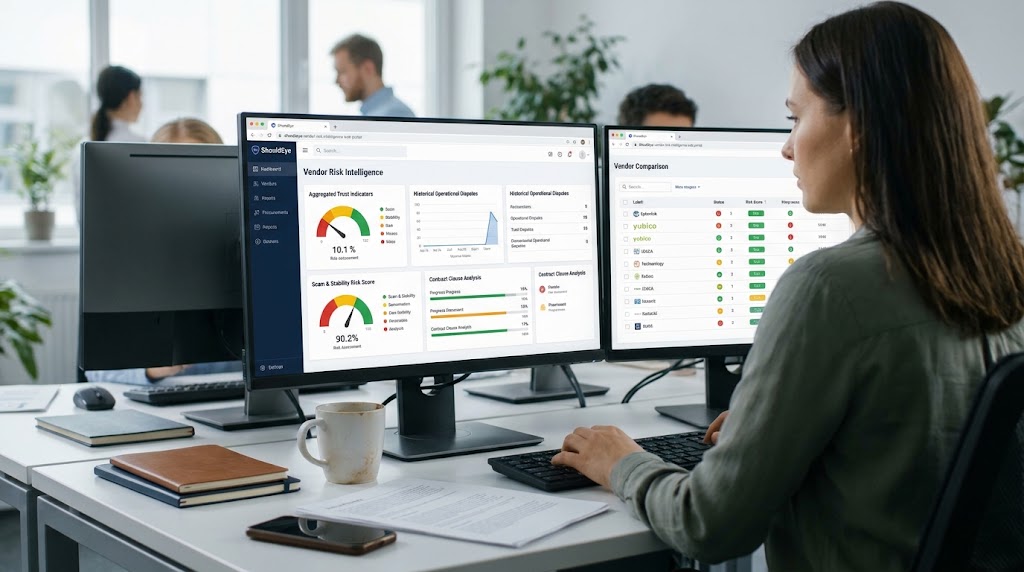
ShouldEye centralizes critical trust indicators by aggregating regulatory filings, user complaints, and contract terms into an accessible portal. When assessing enterprise software, ShouldEye helps teams:
Surface historical operational disputes: Discover patterns involving unresponsive customer support or sudden unilateral revisions to customer data agreements.
Analyze complex contract language: Isolate hidden clauses governing third-party data distribution, liability caps, and log retention.
Compare competitive tools: Contrast deployment criteria for CyberArk, Yubico, ISACA, and other enterprise providers side by side.
Score fraud and stability indicators: Identify warning signals that often precede vendor instability or compliance non-conformance.
Provide automated decision support: Configure ShouldEye to rank verification criteria according to your internal governance requirements.
Leveraging ShouldEye during initial vendor discovery prevents hours of manual document review and provides an objective risk rating before leadership commits capital.
Using EyeQ for Accelerated Contract Due Diligence
EyeQ functions as the contextual research engine integrated directly into ShouldEye. When your security team receives complex vendor whitepapers, terms of service, and license agreements, you can instruct EyeQ to extract all sections related to liability limitations, data residency, and audit rights. EyeQ delivers the relevant contract excerpts in seconds. Furthermore, you can direct EyeQ to benchmark a vendor's machine identity management capabilities against baseline industry standards, generating a structured briefing ready for executive review.
Trends Shaping Zero Trust Architecture Over the Next Decade
The next generation of digital trust tools will be defined by cultural transparency as much as technical protocols. Modern organizations expect verifiable proof at every layer of their technology stack. Key developments reshaping enterprise infrastructure include:
The standard adoption of zero trust architecture, where every network packet and service call undergoes continuous cryptographic validation.
Regulatory formalization of decentralized identity, allowing users and partner firms to exchange verifiable credentials without centralized identity providers.
Mandatory independent verification, elevating structured digital trust assessment from an internal best practice to an enforceable compliance rule.
Selecting modern digital trust tools requires meticulous scrutiny of machine identity management, hardware-backed passkeys, and contractual transparency. Combining a formal evaluation checklist with ShouldEye and EyeQ gives your team the necessary technical visibility to deploy a secure, compliant infrastructure.
Frequently Asked Questions Live
Reader activity for this article, refreshed by EyeQ AI
6 active now 172 total asked 6 questions
1 What is a digital‑trust tool and why do I need one? Trending Trust & Consumer Protection 37 asked Updated 1m ago
2 How can I verify that a vendor’s machine‑identity feature works as advertised? Trending Trust & Consumer Protection 35 asked Updated 2m ago
3 Are hardware‑backed passkeys required for all applications? Popular Trust & Consumer Protection 30 asked Updated 3m ago
4 What should I look for in a digital‑trust self‑assessment questionnaire? Popular Trust & Consumer Protection 26 asked Updated 4m ago
5 Can ShouldEye replace a legal review of vendor contracts? Rising Trust & Consumer Protection 23 asked Updated 5m ago
6 How does EyeQ differ from a regular web search? Rising Trust & Consumer Protection 21 asked Updated 8m ago
About ShouldEye
ShouldEye is an AI-powered trust intelligence platform that helps people evaluate companies, offers, and online experiences through scam checks, policy analysis, complaint signals, and safer alternatives.
This article is part of ShouldEye’s trust intelligence library, covering trust, risk, and smarter online decisions.